Enterprise Web Filtering: How It Works and How It Is Deployed
Enterprise web filtering decides which websites staff, devices and systems may reach, based on each site's category and risk. Companies run it in DNS resolvers, secure web gateways, firewalls, SASE platforms and endpoint agents, and every one of them relies on a URL category database to make the call.
We run the web filter for your library or school
Set one DNS address on your router and every device is filtered: CIPA categories blocked, a staff PIN for adult research, and reports for your records. Nothing to install.
Enterprise web filtering in one minute
Enterprise web filtering is policy-based control of web access across a whole organisation: many sites, thousands of users, managed and remote devices. It blocks threats, enforces the acceptable use policy and shows where web traffic goes.
The direct answer
Every web request is checked against a category database, the category is compared with the policy for that user or group, and the filter allows, blocks, warns or logs. The filtering product enforces the rule; the category data decides what the rule actually catches.
That is why two filters with the same policy can behave very differently: the quality of the category data behind them is not the same.
What happens on every request
Request
A user, device or server asks for a domain, by DNS query or web connection.
Identify
The filter works out who is asking: user, group, device, site or network.
Categorize
The domain is looked up in the category database, often returning several categories.
Decide
The categories meet the policy for that group, plus any allow or deny list entries.
Act and log
Allow, block, warn or log, and record the decision for reports and audits.
Five ways enterprises deploy web filtering
There is no single enterprise web filter. Large organisations place filtering at one or more points in the network, and each point sees a different amount of each request.
| Deployment | Where it sits | What it sees | Strengths | Limits to plan for |
|---|---|---|---|---|
| DNS filtering | The resolver every device uses, on site or in the cloud | The domain name only | Covers every device and protocol, light to roll out, no certificates needed | No paths or uploads; encrypted DNS and hard-coded resolvers can route around it |
| Secure web gateway (SWG) | A proxy, on premises or as a cloud service, that web traffic passes through | Full URLs, file types and uploads when traffic is inspected | Fine-grained rules, warn pages, upload and download controls | Needs traffic steering and certificate trust; privacy exemptions must be planned |
| Next-generation firewall | The network edge of each office or data centre | Domain and server name, more with decryption | Uses hardware already in place; one policy for web and other traffic | Remote users are covered only if their traffic comes back through the office |
| SASE platform | A cloud service combining SWG, CASB, ZTNA and firewall as a service with SD-WAN | Full web traffic for users wherever they work | One policy for office, home and travel; identity-based rules | A larger platform change; the web filter is one part of a wider project |
| Endpoint agent | Software on each managed laptop or phone | Requests from that device, often with app context | Works off-network and on any Wi-Fi; survives network changes | Only managed devices are covered; agents need rollout and updates |
DNS layer plus SWG
DNS filtering catches every device, including printers and IoT, while the gateway handles detailed rules for people browsing.
Firewall plus cloud DNS
Offices filter at the edge they already own; cloud DNS or an agent covers laptops when staff work elsewhere.
SASE plus endpoint agent
Users connect to the cloud service from anywhere, and the agent steers traffic and enforces policy on the device.
Domain Categorization for Enterprise Defense
Enterprise web security has evolved far beyond simple URL blacklists. Modern organizations face a complex threat landscape where employees access thousands of domains daily. A comprehensive categorization database provides the intelligence layer every security stack requires.
Proactive Blocking
Newly registered domains are categorized every day, so suspicious ones can be blocked before an incident, with no signatures needed.
58 Content Categories
Granular classification across adult content, social media, file sharing, gambling, and dozens more categories.
Stack Integration
Feed categorization directly into firewalls, secure web gateways, SIEM platforms, and SOAR playbooks.
Turn your acceptable use rules into switches on a DNS filter
If your goal is to protect your own company rather than ship a security product, we can run the filter and you keep the policy. It reads the same category database that security vendors license.
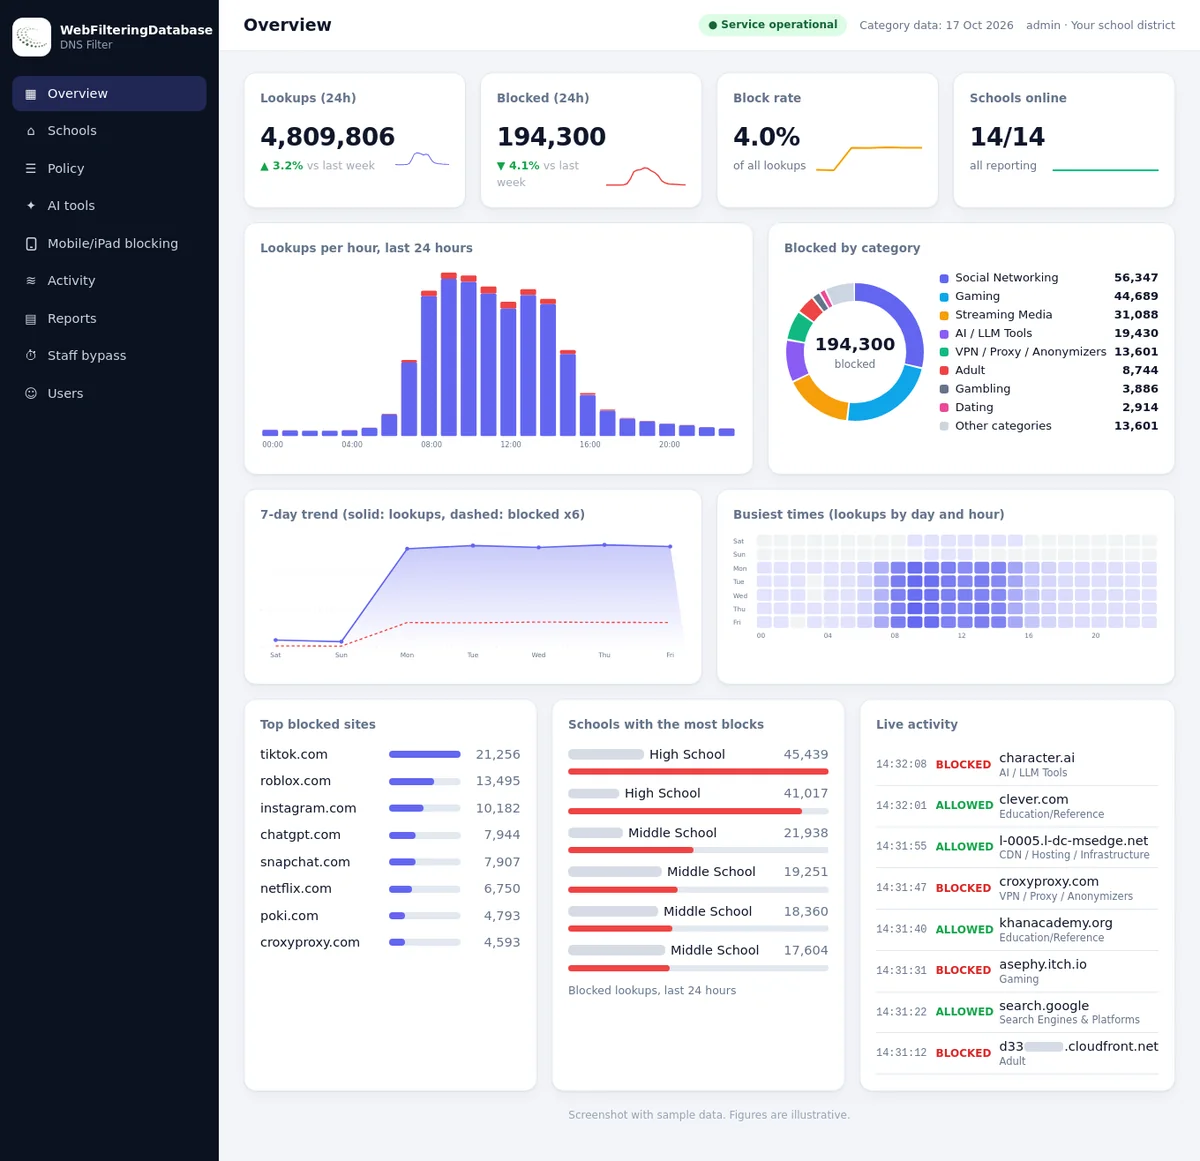
- Set the firewall or router to one DNS address, then choose which of the 22 blocking categories apply at each site.
- Add always-allow and always-block lists for the odd exception, or import the lists you already keep.
- Search the activity afterwards and export it as CSV for audits or HR questions.
Acceptable Use Policy Enforcement
Transform written policies into automated, real-time enforcement with granular domain categorization
Every enterprise maintains an Acceptable Use Policy (AUP) that defines which web resources employees may access during work hours and on corporate devices. Traditionally, enforcing these policies relied on manual audits and employee self-compliance. With a web filtering database, AUP enforcement becomes automated, consistent, and auditable.
- Social media domains can be allowed during break hours but restricted during work periods.
- Gambling, adult content, and illegal activity categories can be permanently blocked.
- Streaming media can be throttled or restricted to preserve bandwidth for business-critical applications.
Category-based policies also adapt to organizational structure.
- Engineering teams may need access to developer forums and code repositories that would be unnecessary for the accounting department.
- Marketing teams require social media access that other departments do not.
Role-Based Policies
Different access rules per department, team, or individual based on job function
Time-Based Controls
Restrict or allow categories during specific hours or business periods
Audit Trails
Complete logging of policy decisions for compliance and HR investigations
Designing enterprise web filtering policy by department
One policy for everyone either blocks too much for some teams or too little for others. Most enterprises start from a company-wide baseline and add department layers on top, using groups from the directory they already run.
| Group | Common starting point | Usual exceptions | Watch for |
|---|---|---|---|
| Company baseline | Block Malware / Phishing / Suspicious, Adult, Illegal Drugs, Hate/Discrimination and Parked / For-Sale Domains | None at this level; exceptions belong to groups | Keep the baseline short, so every group can live with it |
| Finance | Warn on Cryptocurrency, Cloud Storage / File Hosting and personal Email and Messaging | Approved banking and payment portals, audit tools | Payment fraud can start with a look-alike banking page |
| HR and legal | Baseline plus warn on File Sharing/P2P | Job Search/Careers, Social Networking for recruiting | Investigations may need temporary access to blocked content |
| Marketing | Baseline, with social and streaming allowed | Social Networking, Streaming Media, Advertising/Marketing | Ad and tracking domains that other groups block |
| Engineering and IT | Baseline, with developer tools allowed | Developer Tools / Code Hosting, Remote Access Tools for named admins | Remote access tools outside IT are a common attack path |
| Security team | Monitor rather than block for research | Malware and phishing sites from an isolated browser | Keep research access off normal workstations |
| Guest and contractor Wi-Fi | Baseline plus VPN / Proxy / Anonymizers and File Sharing/P2P | None by default | Guest traffic should never reach internal systems |
Five steps to a policy people accept
- 1. Write the baseline firstAgree the short list of categories nobody needs, with HR and legal, before any department asks for changes.
- 2. Run in monitor modeLog for two to four weeks without blocking. Real traffic shows which categories each group actually uses.
- 3. Use warn pagesFor grey areas such as AI / LLM Tools or Cloud Storage, a warning with a reason teaches more than a hard block.
- 4. Time-limit exceptionsEvery allow list entry gets an owner and an end date, so exceptions do not pile up for years.
- 5. Review each quarterCheck blocked-request trends, open exceptions and new categories such as AI tools, then adjust.
Our guide to custom policy management goes deeper on groups and overrides, and corporate web filtering covers policy for whole companies.
Data Loss Prevention & Shadow IT Detection
Identify unauthorized services and prevent sensitive data from leaving your network perimeter
Detecting Shadow IT Through Categorization
Shadow IT, the use of unsanctioned applications and cloud services by employees, is one of the largest security gaps in modern enterprises. It grows fastest where IT oversight is thin.
Category-Driven Data Loss Prevention
Data loss prevention extends beyond endpoint agents. By categorizing the domains employees interact with, security teams can identify potential exfiltration vectors in real time.
Domain categories such as file sharing, paste sites, personal email, cloud storage, and encrypted communications provide the context that traditional DLP systems lack.
- Rather than inspecting every packet for sensitive patterns, category-based DLP focuses on the destinations most likely to be used for unauthorized data transfers, dramatically reducing false positives while maintaining comprehensive coverage.
- Metadata such as technology stack age further enriches this analysis by indicating infrastructure maturity.
Reporting: what enterprise web filtering should show you
Blocking is half the job. The reports decide whether the security team, HR and auditors trust the filter, and every report is grouped by category, so category quality shows up here first.
Top categories by group
Where each department's web time goes. Large shifts point to new tools, new risks or a policy that no longer fits.
Security category hits
Blocked requests to malware, phishing and suspicious domains, by device. Repeated hits from one machine deserve a closer look.
New and unknown domains
Requests to newly registered or rarely seen domains. A high share of unknowns usually means weak category coverage.
AI tool use
Which teams use AI / LLM Tools and how often, so the AI policy rests on facts rather than guesses.
Exception review
Every allow list entry with its owner, reason and end date, ready for the quarterly review.
Exports for other tools
Decision logs with categories attached, sent to the SIEM or kept for audits and HR questions.
Per-user reports touch employee privacy. In some countries monitoring rules or works council agreements apply, so check local requirements before you turn on named reporting.
The services that tend to show up outside the approved list
These are real entries for services employees reach for on their own. Each category can be switched per site or left open for approved teams.
| Destination | How we store it |
|---|---|
| mega.nz | Cloud Storage / File Hosting |
| pastebin.com | Developer Tools / Code Hosting, Cloud Storage / File Hosting |
| gmail.com | Email and Messaging |
| openai.com | AI / LLM Tools |
| slack.com | Email and Messaging |
Integration with SIEM, SOAR & Network Infrastructure
Feed domain intelligence into your existing security operations ecosystem
SIEM Enrichment
Enrich firewall logs, proxy logs, and DNS query logs with domain categories in real time.
- When your SIEM ingests a connection to an unknown domain, the web filtering API instantly returns its category, enabling correlation rules like "alert when any endpoint in the finance VLAN connects to a domain categorized as file-sharing or paste-site outside business hours."
- This transforms raw network telemetry into actionable security intelligence.
SOAR Playbook Automation
Automate incident response with category-aware playbooks.
- When a restricted content email is reported, the SOAR platform can automatically query the web filtering database for every URL in the message, determine categories, and execute the appropriate response: block the domain at the firewall, scan all endpoints that accessed it, notify affected users, and create a ticket for the SOC team, all without human intervention.
Next-Gen Firewall Feeds
Feed category data directly into next-generation firewalls via their external dynamic list or content classification feed mechanisms.
- The firewall can then enforce category-based rules at the network perimeter, blocking connections to unsafe content, and command-and-control domains before traffic even reaches internal systems.
Secure Web Gateway Enhancement
Augment your secure web gateway deployment with additional categorization intelligence.
- The web filtering database provides a second opinion on domain classification, catches newly registered domains that gateway vendors have not yet categorized, and fills gaps in coverage for regional or niche domains that global vendors may miss.
RESTful API Integration
Query domain categories through the lookup API that comes with every licence. JSON responses carry each domain's categories, ranked, so your gateway can apply policy on every request.
Local Database Mirror
For latency-sensitive deployments, run the 120-million-domain database locally and apply the daily delta files. No external API dependency, and filtering continues even during internet outages.
Ready-made Export Formats
Licensed customers can take the data as hosts files, DNS RPZ zones, AdGuard and Pi-hole style lists, firewall external dynamic lists and PAC files, so it drops into the tools already in place.
Enterprise Deployment Architecture
A successful enterprise web security deployment requires careful planning around network topology, user authentication, and failover strategies. The web filtering database supports multiple deployment models to fit any enterprise environment.
Inline Proxy Mode
Deploy as a forward proxy where all HTTP/HTTPS traffic passes through the filtering engine. Each request is categorized in real time, and policy decisions are enforced before the connection is established.
DNS-Based Filtering
Redirect corporate DNS to filtering-enabled resolvers that check domain categories before returning IP addresses. Blocked domains receive an NXDOMAIN or redirect response.
API-Driven Enrichment
Integrate the categorization API into existing security infrastructure. Firewalls, proxies, and SIEM platforms query the API to enrich their native decision-making capabilities.
How a category database feeds enterprise web filtering
Enterprises buy a filter; the filter vendor brings the category data. Some vendors build it, some license it, and some combine their own threat data with a licensed category file.
Category database
Domains with ranked categories, refreshed daily for new domains and monthly for the rest.
Vendor lookup store
The vendor loads the file into its own systems and maps the categories to its product list.
Enforcement point
DNS resolver, gateway, firewall, SASE service or endpoint agent answers each request locally.
Enterprise policy
The customer switches categories per group and sees the result in blocks and reports.
Why category data quality decides the result
Enterprise buyers judge a filter by what it blocks and what it misses, not by the data behind it. For vendors, every gap in the data turns into a support ticket or a lost renewal.
| Data problem | What the enterprise sees | What it costs the vendor |
|---|---|---|
| New domains not covered | A fresh phishing site loads, or a new business tool is blocked as unknown | Security incidents traced back to the filter, and helpdesk noise |
| Wrong primary category | A tool a team needs is blocked under a category it does not belong to | Tickets, manual exceptions and doubts about every other block |
| One category per site | A gaming site with betting features passes a Gambling block | Policy gaps that customers find before the vendor does |
| Stale labels | A domain that changed owner or became parked keeps its old category | Wrong decisions on sites that are now risky or empty |
| Weak coverage outside English | Regional sites show up as uncategorized in local offices | Harder sales in regions where the data is thin |
| Missing new categories | No clean way to report on or control AI tools | Customers ask for a category the product cannot offer |
120 million domains
Categorized in 58 web filtering categories, with the IAB Content Taxonomy in the same file.
About 300,000 a day
Newly registered domains categorized daily, then checked again after a week and after a month.
Several categories per site
Ranked by how much of the site each one describes, so secondary risks stay visible to policy.
Runs inside the product
CSV, Parquet or JSON files, on premises or air-gapped, with a lookup API included in licences.
Building a filter, gateway or SASE service? See the web filtering database, OEM licensing and the web filter lookup to check how we categorize the domains your customers care about.
Remote laptops and networks that rewrite DNS
A private encrypted link keeps laptops and phones under the same rules when they leave the building, and also where a provider redirects DNS. The managed filter needs no appliance or agent on your side, and one dashboard covers many sites.
Enterprise Security Use Cases
Real-world applications of domain categorization in enterprise environments
Financial Services
Banks and investment firms use domain categorization to prevent access to unauthorized trading platforms, block cryptocurrency exchanges on trading floor networks, and ensure compliance with SEC and FINRA regulations around electronic communications and data handling.
Healthcare Organizations
Hospitals and healthcare networks enforce HIPAA requirements by blocking access to personal cloud storage, restricting social media on clinical workstations, and preventing staff from accessing domains that could introduce ransomware into systems containing protected health information.
Manufacturing & Critical Infrastructure
Industrial environments use domain categorization to segment OT networks from IT networks, ensuring that industrial control systems can only communicate with approved vendor domains. Any connection attempt to an uncategorized or suspicious domain triggers an immediate alert.
Schools & Education
Schools are among the most targeted institutions for cyberattacks, and they face the same web security challenges as enterprises, combined with a duty to protect students. Districts deploy the best web filter for schools and school districts to combine threat blocking with age-appropriate content policies.
Enterprise web filtering checklist
Use these questions when comparing enterprise web filtering products, or when reviewing the one you already run. Each answer depends partly on the product and partly on the category data inside it.
- Remote coverage: are laptops filtered at home, in hotels and on mobile data, not only in the office?
- Bypass handling: does the product deal with encrypted DNS, VPN apps and proxy sites that route around it?
- Category depth: does it separate AI tools, file sharing, personal email and remote access, or lump them together?
- Several categories per site: can a policy act on a secondary category, such as betting inside a gaming site?
- New domains: how fast are newly registered domains categorized, and what happens to unknown ones meanwhile?
- Exceptions: can admins add scoped, time-limited allow and deny entries with an owner and reason?
- Inspection exemptions: can banking, health and other private categories skip decryption?
- Reporting and export: are decisions logged with categories, and can they flow to the SIEM?
- Groups and sites: do policies follow directory groups and work across many offices?
- Test before rollout: can you look up your critical business sites and see how they are categorized?
Common mistakes in enterprise rollouts
Blocking all unknown domains
Safe on paper, but with weak data it breaks new business tools daily. Warn or isolate unknowns instead, and judge coverage first.
Inspecting everything
Decrypting banking, health and personal email traffic raises privacy issues. Exempt those categories from inspection by design.
One policy for all
A single rule set forces either constant exceptions or weak protection. Groups from the directory fix this at the start.
Ignoring DNS bypass
Browsers and apps with their own encrypted DNS can skip a DNS filter. Control it with device settings, firewall rules or an agent.
Exceptions that never expire
Old allow list entries become blind spots. Give every exception an end date and review the list each quarter.
Testing only famous sites
Every filter knows the top brands. Test your own suppliers, regional sites and new domains, where data quality shows.
Related reading: DNS over HTTPS and web filtering, SSL inspection and URL categories and web filtering software for business.
API Integration for Enterprise Security
Integrate domain categorization into your enterprise security stack with just a few lines of code
Enterprise Security Policy Enforcement
Classify domains against corporate policy categories and take automated action: block, allow, or flag for review.
import requests

API_URL = "https://webfilteringdatabase.com/api/moderate.php"
API_KEY = "YOUR_API_KEY"

# Categories blocked by corporate acceptable use policy
BLOCKED_CATEGORIES = {
    "Adult Content", "Gambling", "Weapons",
    "Drugs", "Malware", "Phishing"
}

def enforce_policy(domain):
    result = requests.post(API_URL, json={
        "api_key": API_KEY,
        "query": domain
    }).json()

    categories = set(result.get("categories", []))

    # Check against corporate AUP categories
    violations = categories & BLOCKED_CATEGORIES
    if violations:
        return "BLOCK", f"Policy violation: {', '.join(violations)}"

    return "ALLOW", result.get("primary_category", "Uncategorized")

# Enterprise firewall integration example
domains_to_check = ["slack.com", "poker-site.xyz", "drive.google.com"]
for domain in domains_to_check:
    action, reason = enforce_policy(domain)
    print(f"{action}: {domain} ({reason})")
const API_URL = 'https://webfilteringdatabase.com/api/moderate.php';
const API_KEY = 'YOUR_API_KEY';

const BLOCKED_CATEGORIES = new Set([
    'Adult Content', 'Gambling', 'Weapons',
    'Drugs', 'Malware', 'Phishing'
]);

async function enforcePolicy(domain) {
    const response = await fetch(API_URL, {
        method: 'POST',
        headers: { 'Content-Type': 'application/json' },
        body: JSON.stringify({ api_key: API_KEY, query: domain })
    });
    const result = await response.json();

    // Check AUP category violations
    const violations = (result.categories || [])
        .filter(c => BLOCKED_CATEGORIES.has(c));
    if (violations.length) {
        return { action: 'BLOCK', reason: violations.join(', ') };
    }

    return { action: 'ALLOW', reason: result.primary_category };
}

// Check enterprise traffic
['slack.com', 'poker-site.xyz', 'drive.google.com']
    .forEach(async (d) => {
        const { action, reason } = await enforcePolicy(d);
        console.log(`${action}: ${d} (${reason})`);
    });
# Classify a domain for enterprise policy enforcement
curl -X POST "https://webfilteringdatabase.com/api/moderate.php" \
  -H "Content-Type: application/json" \
  -d '{
    "api_key": "YOUR_API_KEY",
    "query": "slack.com"
  }'

# Example response:
# {
#   "domain": "slack.com",
#   "primary_category": "Business",
#   "categories": ["Business", "Technology", "Messaging"]
# }

# Check a suspicious domain
curl -X POST "https://webfilteringdatabase.com/api/moderate.php" \
  -H "Content-Type: application/json" \
  -d '{
    "api_key": "YOUR_API_KEY",
    "query": "poker-site.xyz"
  }'
<?php
// Enterprise web security policy enforcement
$apiUrl = 'https://webfilteringdatabase.com/api/moderate.php';
$apiKey = 'YOUR_API_KEY';

$blockedCategories = ['Adult Content', 'Gambling', 'Weapons', 'Drugs', 'Malware'];

function enforcePolicy($domain, $apiUrl, $apiKey, $blocked) {
    $ch = curl_init($apiUrl);
    curl_setopt($ch, CURLOPT_POST, true);
    curl_setopt($ch, CURLOPT_POSTFIELDS, json_encode([
        'api_key' => $apiKey,
        'query'   => $domain
    ]));
    curl_setopt($ch, CURLOPT_HTTPHEADER, ['Content-Type: application/json']);
    curl_setopt($ch, CURLOPT_RETURNTRANSFER, true);
    $result = json_decode(curl_exec($ch), true);
    curl_close($ch);

    // Check AUP violations
    $violations = array_intersect($result['categories'] ?? [], $blocked);
    if (!empty($violations)) {
        return ['BLOCK', implode(', ', $violations)];
    }

    return ['ALLOW', $result['primary_category'] ?? 'Uncategorized'];
}

// Enterprise gateway integration
$domains = ['slack.com', 'poker-site.xyz', 'drive.google.com'];
foreach ($domains as $d) {
    [$action, $reason] = enforcePolicy($d, $apiUrl, $apiKey, $blockedCategories);
    echo "$action: $d ($reason)\n";
}
?>
Stack integration or a filter that is already running
For many companies the real question is how much of the web control they want to build and operate.
| Need | Wire the database into your stack | Managed DNS filter |
|---|---|---|
| Time to first block | Depends on your integration work | One DNS address on the router or firewall |
| Staff who need research access | You build the exception flow | PIN bypass for 15, 30 or 60 minutes, logged, and it reverts |
| Many branches | Replicate policy yourself | One dashboard, separate settings per site |
| Evidence for compliance | Pipe logs into your own tools | Searchable activity, reports and CSV exports |
| Category depth | Same 120M+ domain database | Same database, 22 blocking categories per site |
Enterprise web filtering FAQ
What is enterprise web filtering?
The controls a company uses to decide which websites staff, devices and systems may reach, based on each site's category and risk. It runs in DNS resolvers, secure web gateways, firewalls, SASE platforms and endpoint agents.
Do enterprises need DNS filtering or a secure web gateway?
Often both. DNS filtering covers every device and protocol cheaply but sees only the domain, while a secure web gateway sees full URLs and uploads but needs traffic routed through it.
How does web filtering cover remote employees?
Through a cloud service the device connects to, such as a SASE platform or cloud DNS filter, or through an endpoint agent on the laptop. Traffic sent back over a VPN to the office firewall also works but adds delay.
Does enterprise web filtering require SSL inspection?
Not for category decisions on the domain, which DNS queries and the TLS server name usually reveal. Inspection is needed for path rules, upload controls and content scanning, and many teams exempt banking and health sites for privacy.
How many categories does an enterprise web filter need?
Enough to separate risks that policies treat differently, such as AI tools, file sharing, personal email and newly seen domains. Our database uses 58 web filtering categories and allows several per domain.
Where does the category data in a web filter come from?
Filter vendors build a URL category database, license one, or combine both. The enterprise sees the result as the category behind every allow or block decision.
Pricing follows the number of sites and devices you want covered. Start with a pilot on a single site, and read the blocks and reports before you commit the rest of the company.
Secure Your Enterprise with Domain Intelligence
Leverage 120 million categorized domains and 58 content categories to build a comprehensive enterprise web security strategy.