URL category data for VPN apps: protection toggles and split tunnelling
VPN and privacy apps increasingly sell more than a tunnel: tracker blocking, a family mode, content switches and smart routing. This guide is for VPN product teams who want those features to be accurate and current, decided on their own resolvers or on the device, without logging what users do.
Protection settings
From a toggle in the app to a category in the data
Every protection setting a user sees maps to one or more categories. Defining that map is the main product decision; the data does the rest.
| Setting in the app | Categories behind it | Design note |
|---|---|---|
| Block ads and trackers | Advertising/Marketing | Use the main category, or analytics tools that apps depend on break |
| Block adult content | Adult, optionally Lingerie/Swimsuits/Intimate Apparel | Any-match: a domain with Adult anywhere is blocked |
| Block gambling | Gambling | Gambling often pairs with Gaming; block Gambling itself |
| Family mode | Adult, Gambling, Dating, Weapons, Illegal Drugs, Violence, Hate/Discrimination | Add SafeSearch on search engines if your resolver supports it |
| Block AI chat apps | AI / LLM Tools | Popular with parents and some employers |
| Banking outside the tunnel | Online Banking | See split tunnelling below |
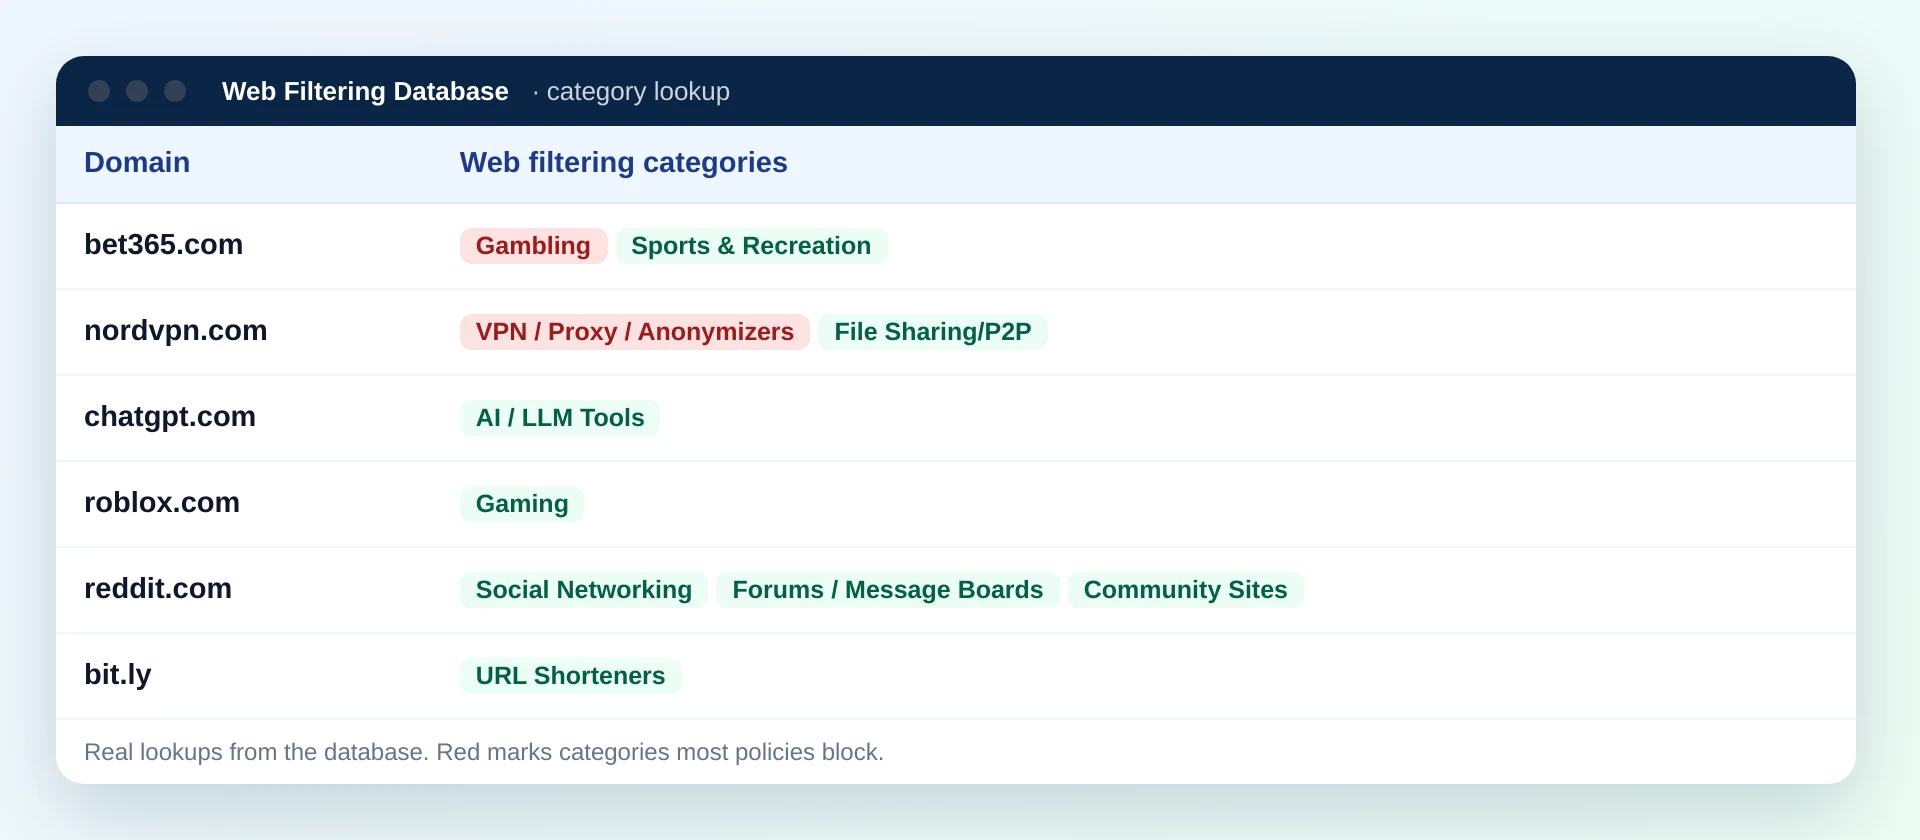
Power every protection switch in your VPN from one category file
Licence holders load our database on their own resolvers or ship a compact subset inside the app. Each toggle maps to categories from the same 58-category taxonomy, and daily deltas keep new tracker, gambling and adult domains covered.
- Decisions made on your infrastructure, nothing sent to a third party.
- Popularity-ranked subsets sized for phones.
- Several categories per domain for precise toggles.
On your resolvers or on the device
Both work. Most providers start on the resolver and add an on-device list later for speed or for connections where the tunnel is off.
On your DNS resolvers
The tunnel already sends DNS to your servers. They load the full file and decide each lookup against the user's settings.
- The full database, every category
- Changes apply to every user at once
- Nothing extra in the app download
- Settings travel with the account, not the device
On the device
The app carries a compact list and decides locally, even when the tunnel is paused.
- A popularity-ranked subset of the blocked categories
- Works offline and with the tunnel off
- Daily deltas pushed as small updates
- Keeps lookups on the phone entirely
Sizing an on-device list is a numbers question. Our counts for the 20 million most visited domains, such as the categories behind a family set, are in what the web is made of.
Five domains and the setting that would act on each
Real rows from our data. The same rows drive a blocking toggle for some domains and a routing rule for others.
| Domain | Categories in our data | Setting that acts on it |
|---|---|---|
| criteo.com | Advertising/Marketing | Block ads and trackers |
| outbrain.com | Advertising/Marketing | Block ads and trackers |
| appsflyer.com | Advertising/Marketing, Business, Web-based Applications | Tracker toggle; test apps that use it for sign-up links |
| chase.com | Financial Services, Online Banking | Banking outside the tunnel |
| revolut.com | Financial Services, Online Banking | Banking outside the tunnel |
Category-based split tunnelling
Users often need some traffic outside the tunnel. Letting them choose by category is simpler for them and easier to keep current than lists of domains.
Online banking
Some banks challenge or block logins from VPN addresses. Routing Online Banking outside the tunnel avoids the support tickets.
Local streaming
Users who want their home country's catalogue on Streaming Media can keep it outside the tunnel while everything else stays inside.
Work tools
Web-based Applications and company sites that expect an office address can bypass a personal VPN on a work laptop.
Split tunnelling by category relies on the DNS answer: the app sees which category a name belongs to and routes the connection that follows. Explain plainly to users which traffic leaves the tunnel.
Privacy by design: deciding without logging
A no-logs promise and content blocking can live together, as long as the decision happens on your side and leaves nothing behind.
Local lookups
The database sits on your resolvers or in the app; no lookup goes to an outside service.
No per-user record
A decision needs the domain and the user's settings, not a stored history.
Counts, not logs
If you want metrics, keep totals per category and day, never per user.
Clear wording
Tell users that blocking happens on your servers or their phone, and that nothing is shared.
How the licensed database fits a no-logs VPN
The data arrives as files that run inside your own systems, with the lookup API only as an optional extra for domains not yet in your copy. Your resolvers can decide every lookup locally, so the protection features add no new party that sees your users' traffic.
What categories do not cover
Be clear in your product about what each feature is. Categories describe what a site is; they are not a threat feed, and users trust apps that say so.
| Feature users ask for | Category data | What else it needs |
|---|---|---|
| Block known malware and phishing addresses | Not the right tool on its own | A threat feed updated through the day |
| Block a single page of a site | Decides by domain only | Inspection inside the encrypted connection, which most VPNs avoid |
| Block ads inside an app's own servers | Only where ads use separate domains | Nothing else; some ads cannot be blocked by DNS |
| Age ratings for apps | Not covered | App store ratings and parental controls |
Six product mistakes with VPN blocking features
Each of these shows up in app store reviews within weeks of launch, and each is easy to avoid with a little planning.
Any-match for trackers
Blocking every domain that carries Advertising/Marketing anywhere breaks analytics and sign-in links. Use the main category.
No allow list for users
Every blocking feature needs a way for the user to unblock one site.
A stale on-device list
Lists shipped only with app updates fall weeks behind. Push daily deltas.
Calling it malware protection
A content category is not a threat feed. Name features by what they do.
Breaking captive portals
Hotel and airport sign-in pages must open before the tunnel; keep them out of every rule.
Silent blocks
Show the user which setting blocked a site, so they can change it instead of leaving.
Sensible defaults for a consumer VPN
Defaults decide what most users experience, because few people ever open the settings screen. A cautious starting point that respects adult users:
| Setting | Default | Why |
|---|---|---|
| Block ads and trackers | On | The feature most users expect from a privacy app |
| Block adult content | Off | Adults choose for themselves; offer it clearly in settings |
| Family mode | Off, prompted on family plans | Parents switch it on for children's devices |
| Block gambling | Off | Valued by people avoiding gambling; never forced |
| Banking outside the tunnel | Off, suggested after a failed bank login | Solves a real problem at the moment it appears |
Resolver integration in six steps
A typical path for a team that already runs its own DNS resolvers. Most of the work is in steps two and four, where product decisions meet the data.
1. Load the file
Import the category file into the resolver's memory or a fast local store.
2. Map settings
Write down which categories each toggle covers, as in the table above.
3. Carry settings
Pass the user's toggles to the resolver with the session, not in a log.
4. Decide in order
The user's own allow list first, then their block list, then categories.
5. Apply deltas
Merge the daily file of new domains without restarting the resolver.
6. Count, do not log
Keep totals per category for product decisions, never per user.
Test with users
Run a beta group and read support tickets before switching defaults.
Plan the unknowns
Decide what the resolver does with domains not yet in the file.
Protection features from public lists, or from a licensed category database
The same toggles, built two ways.
| For a VPN product | Public lists | Licensed category database |
|---|---|---|
| Toggles beyond ads | A separate list for each, if one exists | Any of 58 categories, one definition each |
| Split tunnelling by category | Lists of bank domains kept by hand | Online Banking and other categories ready to route |
| Right to ship it | Different terms for each list | One OEM licence covering resolvers and app |
| New domains | Whenever maintainers add them | About 300,000 categorized every day |
| On-device size | Whatever the list happens to be | Subsets ranked by popularity |
Category data for VPN apps: frequently asked questions
How do VPN apps add content blocking features?
Most answer DNS lookups on their own resolvers. When a user switches on a toggle such as tracker blocking or family mode, the resolver returns an empty answer for domains in the matching categories.
Does category blocking require logging users' browsing?
No. With the category database loaded on your own resolvers, each lookup is decided locally and nothing has to be stored or sent to a third party, which suits no-logs services.
What is category-based split tunnelling?
Letting users send whole categories of sites outside the VPN tunnel, for example online banking that rejects VPN addresses, instead of listing every bank's domain by hand.
Can the blocking run on the device instead of the server?
Yes, with a compact list. A popularity-ranked subset of the categories you block fits on phones, and daily delta files keep it current.
Does category data protect against malware sites?
Categories describe what a site is, such as adult, gambling or advertising. Known malicious addresses change by the hour and need a threat feed next to the category data.
Should tracker blocking be on by default?
For a privacy app, usually yes, with a clear way to unblock a site. Use the main category so analytics and sign-in services that many apps depend on are not caught by a secondary label.
How fresh do the lists need to be?
Tracker, gambling and adult domains change constantly. About 300,000 newly registered domains are categorized every day, so daily delta files keep resolver and on-device lists current.
Can business VPN customers set their own rules?
Yes, if your product supports it. Store a policy per business account, map it to categories the same way as the consumer toggles, and let the account admin manage an allow list for their own staff.
What licence does a VPN provider need?
An OEM licence that covers embedding the data in a product you sell, whether it runs on your resolvers or inside the app. We quote it per deployment, based on users and delivery.
Database licences start at $999 for the 1 million most popular domains, and OEM licences for VPN products are quoted per deployment, by users and delivery method. Tell us whether filtering runs on your resolvers or in the app, and we will scope it.
Give every protection toggle a real category behind it
Tell us which features you plan, where filtering runs and how many users you have. We will propose the categories, the delivery and the OEM licence.
Domain names in the tables identify services for illustration only. Web Filtering Database is not affiliated with, sponsored or endorsed by their owners.